Google and Industry Partners Dismantle Massive XCPE Botnet Infecting Millions of Android TV Boxes

In a landmark cybersecurity operation, Google, working in tandem with a coalition of global industry partners, has successfully dismantled the XCPE botnet, a malicious infrastructure that had compromised more than 1.3 million Android TV set-top boxes. The operation represents a significant blow to a sophisticated supply-chain attack that saw devices shipped from the factory pre-installed with malware designed to facilitate advertising fraud and surreptitious "residential proxy" operations. Security researchers suggest the scale of the operation is likely far larger than the initial count, with the takedown effectively severing connectivity to an estimated 10 million additional compromised Internet of Things (IoT) devices, ranging from digital signage systems and karaoke machines to specialized healthcare hardware.
The investigation, spearheaded by the Google Threat Intelligence Group (GTIG), identified the root of the infection as Videostrong Technology Co., a China-based manufacturer. The findings confirm that Videostrong deliberately embedded malicious code into the firmware of their set-top boxes. This code, which the GTIG dubbed "XCPE" after one of its core components, remained dormant until the devices were first connected to the internet, at which point it automatically activated, enrolling the hardware into a global network of "residential proxies."
The Mechanics of the XCPE Infection
The XCPE botnet functioned as a parasitic layer atop the legitimate Android TV operating system. By hijacking the internet connections of residential users, the botnet enabled third-party customers to rent these compromised IP addresses. Such services are frequently marketed as tools for legitimate web traffic anonymization or location spoofing, but in the hands of malicious actors, they are weaponized for account takeover (ATO) attacks, large-scale advertising fraud, and aggressive automated content scraping—often to fuel the development of Large Language Models (LLMs) or other AI-driven projects.
Evidence provided by GTIG indicates that Videostrong did not merely infect devices but actively monetized the backdoor by selling access to criminal syndicates. These affiliates were then granted the ability to push additional malware modules onto the compromised devices, effectively turning millions of living-room televisions into unwitting nodes for a global criminal infrastructure.
Chronology of Discovery and Takedown
The uncovering of the XCPE botnet is the culmination of a broader, multi-year effort to secure the fragmented and often insecure IoT market. The timeline of this threat can be traced back to early 2026, when researchers began noting a surge in anomalous traffic patterns originating from Android TV hardware.

- January 2026: Synthient, a security startup specializing in proxy network tracking, publishes critical research regarding the "Kimwolf" botnet. This botnet was responsible for record-breaking Distributed Denial of Service (DDoS) attacks. Synthient’s research demonstrated that Kimwolf was exploiting vulnerabilities in the software development kits (SDKs) used by various residential proxy providers to infect devices on local networks.
- June 2026: The FBI, in collaboration with international partners, seizes hundreds of domains associated with NetNut, a subsidiary of the Israeli firm Alarum Technologies. The seizure was part of an operation against the "Popa" botnet, which had similarly enslaved TV boxes to operate as residential proxies.
- October 2026: The industry continues to consolidate as Oxylabs and Honeygain reorganize under a new umbrella entity, "Source," supported by a $3.6 billion valuation and $130 million in funding from Warburg Pincus.
- November 2026: Google officially announces the takedown of the XCPE infrastructure. Through legal action and technical cooperation with ISPs and infrastructure providers, Google seized the command-and-control (C2) domains used by Videostrong to manage the infected boxes.
Supporting Data and Industry Implications
The scale of the threat is underscored by the diversity of the affected hardware. While Android TV boxes were the primary target, the modular nature of the XCPE malware allowed it to jump to other IoT devices sharing the same Android-based firmware architecture. Reports from Synthient specifically highlighted the "MECOOL" line of streaming boxes, manufactured by Skyworth Technology, as having been bundled with the same malicious software as the Videostrong units.
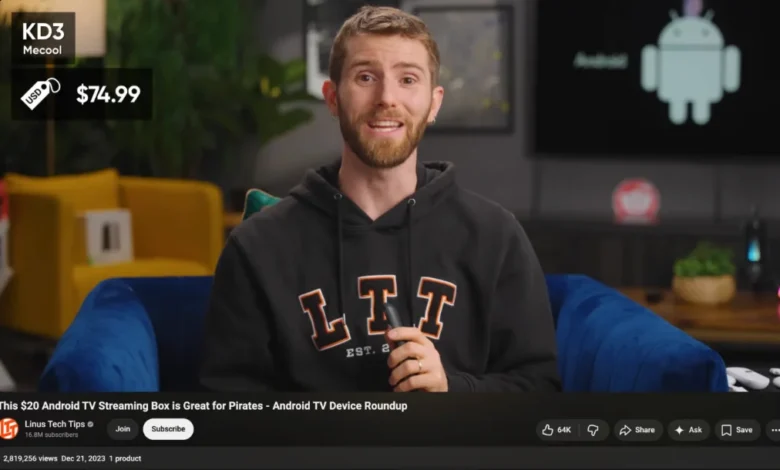
The popularity of these devices was not accidental. Many of the infected units were heavily promoted by social media influencers on platforms like TikTok and YouTube. These influencers often touted the devices for their ability to provide access to hundreds of premium, pirated streaming services for a single, one-time fee. The influence of these marketing campaigns was profound; one popular YouTube channel, Linus Tech Tips, featured the MECOOL device in 2023. Following revelations of the device’s malicious nature, the channel issued a public statement clarifying that it had updated its content to label the device as a scam and removed all associated affiliate links.
Official Responses and Accountability
The revelation that a hardware manufacturer would intentionally install malware has sent shockwaves through the consumer electronics industry. Google has stated that it requires all Android device makers to undergo rigorous security and compatibility testing; however, Videostrong managed to circumvent these protocols by deploying the malicious payload immediately after the user performed the initial device setup, effectively bypassing the factory-state security checks.
Oxylabs, whose SDKs were frequently implicated in the XCPE ecosystem, issued a statement following the takedown. The company defended its business model by claiming that its systems are designed to require user consent before a device can function as an exit node. However, they acknowledged that malicious developers, such as those at Videostrong, had successfully faked these consent signals.
"We have been conducting regular audits of the applications provided by our partners," the Oxylabs statement read. "However, following this incident, we will improve the application and the build fingerprinting logic to better detect cases where the SDK is running on an unapproved build of an authorized application." Oxylabs further confirmed they had suspended their relationship with a supplier identified as "com.abc.nexus," which had been linked to the malware distribution.
Broader Context: The Residential Proxy Economy
The rise of the "residential proxy" as a service has created a significant incentive for botnet operators. Because residential IPs appear to websites as legitimate home internet users rather than data center traffic, they are highly prized by bad actors.

This business model—whereby device owners are unknowingly turned into the product—has become a lucrative, if ethically dubious, industry. The involvement of venture capital, such as the investment in "Source," highlights the tension between the legitimate use of proxy networks for tasks like market research and their exploitation for cybercrime.
The takedown of XCPE serves as a critical case study in the risks of the "grey market" hardware ecosystem. Millions of users, seeking inexpensive alternatives to legitimate streaming hardware, were unknowingly trading their network security for access to pirated content.
Analysis of Future Risks
While the XCPE botnet has been dismantled, the underlying vulnerabilities remain a concern for the security community. The ease with which manufacturers like Videostrong and Skyworth could embed backdoors into firmware suggests that current certification processes may be insufficient to handle the complexities of the modern IoT supply chain.
Security analysts emphasize that the 1.3 million devices identified by Google are likely only the "tip of the iceberg." Because the proxy modules are designed to be modular and adaptable, the criminal affiliates behind these botnets possess the agility to pivot to new delivery mechanisms.
Moving forward, industry experts call for:
- Stricter Supply Chain Audits: Greater scrutiny of firmware integrity from original design manufacturers (ODMs).
- Increased Transparency: Clearer disclosures regarding the software components bundled into consumer IoT devices.
- Enhanced Consumer Awareness: Greater education regarding the risks of "jailbroken" or non-certified streaming hardware.
As Google continues to refine its security protocols for Android-based devices, the XCPE incident remains a stark reminder that in the interconnected landscape of modern electronics, the most significant threat to a user’s network security may be the device they have placed at the center of their home entertainment system. The successful disruption of this botnet is a victory for digital safety, but the resilience of the residential proxy economy suggests that the battle against supply-chain-embedded malware is far from over.
Related posts: