Chinese State-Sponsored Threat Group Vapor Panda Scales Global Cyber Espionage Operations Using ARTEX AI Framework

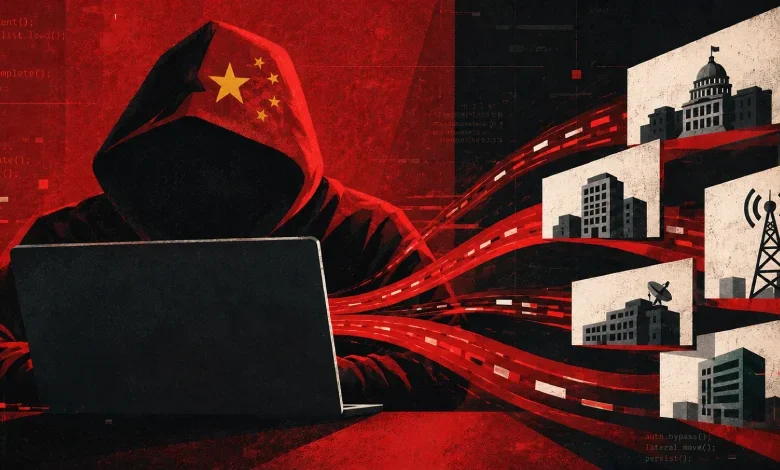
A sophisticated Chinese state-sponsored cyber espionage group known as Vapor Panda has dramatically expanded its global intelligence-gathering operations through the deployment of an advanced, Go-based artificial intelligence penetration testing framework called ARTEX. Cybersecurity researchers at CrowdStrike and Zscaler have documented a massive surge in simultaneous, highly automated cyberattacks targeting critical infrastructure, foreign ministries, and defense contractors across multiple continents. This technological leap represents a major escalation in how state-backed threat actors leverage agentic artificial intelligence to multiply their operational capacity, allowing small human teams to execute complex, multi-vector intrusions at an unprecedented scale and speed.
The campaign, which intensified significantly in late 2026, highlights a dangerous new frontier in cyber warfare. By integrating commercial large language models (LLMs) like DeepSeek with customized, autonomous planning and execution agents, threat actors can bypass traditional limitations of manual exploitation. Cybersecurity analysts warn that this capability fundamentally shifts the economics of cyber espionage, lowering technical barriers and enabling persistent, coordinated attacks against hundreds of high-value targets concurrently.
Origins and Attribution of Vapor Panda
Vapor Panda, historically tracked by various threat intelligence firms under alternative monikers including VexatiousTemper and exhibiting strong operational overlaps with Trend Micro’s Earth Estries cluster, first surfaced on the global threat landscape around February 2021. Over the years, the group has established a reputation for conducting highly targeted, stealthy intrusions directed at government entities, telecommunications providers, think tanks, and technology firms. Their primary mission traditionally centers on strategic intelligence collection, long-term persistence, and the theft of sensitive intellectual property in alignment with geopolitical interests originating from the People’s Republic of China.
The emergence of Vapor Panda as a primary adopter of agentic AI frameworks marks a tactical evolution. Rather than abandoning their established access-development methodologies, the group has utilized ARTEX as a force multiplier. This integration allows a limited number of human operators to manage hundreds of active intrusion engagements simultaneously, a feat that would previously have required massive teams of human hackers working around the clock.
Chronology of the 2026 ARTEX Campaign

The large-scale deployment of the ARTEX framework by Vapor Panda followed a carefully orchestrated timeline characterized by rapid expansion and aggressive automated reconnaissance:
February 2021: Initial threat clusters associated with Vapor Panda (VexatiousTemper and Earth Estries) are first identified by global cybersecurity researchers conducting post-incident analysis on targeted government networks.
April 2026: Security researchers detect concurrent intrusions linked to related Chinese state-sponsored clusters, such as Titan Panda, targeting legal entities in North America using sophisticated in-memory frameworks.
October 17, 2026: Vapor Panda launches a massive, synchronized wave of automated intrusions utilizing the ARTEX framework, targeting more than 200 distinct organizations worldwide within a compressed operational window.
Late October 2026: Rapid adoption of ARTEX by multiple distinct threat actors prompts its primary developer, Li Puhua (tracked as "Autumn-27"), to transition the project from open-source to closed-source status in an attempt to retain control over the powerful tool.
November 2026: Leading cybersecurity firms, including CrowdStrike and Zscaler, publish comprehensive threat intelligence reports detailing the architecture, token consumption metrics, and global impact of agentic AI-driven cyber attacks.
The Mechanics of ARTEX and Agentic AI in Cyberattacks
At the core of Vapor Panda’s late-2026 campaign is the ARTEX framework, written in the Go programming language and designed to orchestrate multiple LLM backends autonomously. According to technical analyses released by Zscaler ThreatLabz and CrowdStrike, ARTEX utilizes a hierarchical structure composed of "planner" and "worker" agents. These autonomous agents communicate and coordinate internally to achieve high-level operational goals set by a human controller.
When deployed against a target network, the ARTEX framework executes a continuous loop of reconnaissance, vulnerability identification, exploitation, and lateral movement. The AI agents are capable of shifting tactics dynamically; if one specific attack path—such as a web application vulnerability or a cloud service misconfiguration—fails, the planning agents automatically pivot to alternative vectors spanning Active Directory, container environments, mail servers, and VPN infrastructure.
CrowdStrike telemetry revealed the sheer scale of computation involved in these automated operations. In a single intrusion analyzed by researchers, Vapor Panda’s planning agents consumed approximately 1.4 billion input tokens. This staggering volume underscores the deep reliance on large language models, driven by integrations with platforms like DeepSeek and subscription-based commercial LLMs, to maintain persistent, complex decision-making loops without continuous human intervention.
A human operator remains in the loop primarily to oversee strategic objectives, authorize high-impact actions, and steer the autonomous agents past sophisticated endpoint detection and response (EDR) sensors. Through this human-AI collaboration, operators have successfully directed agents to author custom web shells, extract domain administrator credentials, and systematically enumerate network security coverage.

Global Targeting and Confirmed Compromises
The geographic and sector-specific scope of the Vapor Panda campaign is vast, reflecting comprehensive intelligence-gathering priorities. Starting in mid-October 2026, the threat group initiated automated scanning, credential harvesting, and password-spraying attacks against more than 200 organizations globally.
Among the primary targets identified by security analysts are:
Foreign Ministries and Diplomatic Missions: Located across Latin America, Europe, Asia, and the Middle East, representing a clear intent to gather geopolitical and diplomatic intelligence.
Defense and Semiconductor Sectors: High-value technology and military industrial base organizations situated primarily within the United States.
Think Tanks and Policy Institutes: Prominent U.S.-based research organizations frequently targeted for policy insights and strategic foresight data.
Telecommunications Providers: Multi-region telecom networks offering broad visibility into global communications traffic.
Post-exploitation activities have been formally confirmed across at least nine distinct organizations. In these successful breaches, Vapor Panda deployed BLOODALCHEMY—a sophisticated derivative of the well-known ShadowPad malware family—followed by aggressive network reconnaissance, credential spraying, and lateral movement. Additionally, password-spraying and credential-scanning campaigns were directed at a minimum of 12 supplementary targets, including European government entities and American policy groups.
Broader Threat Landscape: The Rise of Additional Panda Clusters
The disclosure of Vapor Panda’s AI-driven operations coincides with broader intelligence findings from CrowdStrike’s annual threat hunting reports, which identified four previously undocumented China-linked state-sponsored threat clusters: Hollow Panda, Overcast Panda, Titan Panda, and Veiled Panda. These groups demonstrate the multifaceted nature of state-directed cyber espionage, utilizing diverse techniques ranging from physical proximity intrusions to zero-day exploitation.
Overcast Panda has been singled out as an exceptionally persistent threat facing international organizations with personnel traveling to mainland China. The group specializes in close-access intrusions, physically deploying their proprietary FlowCloud backdoor directly onto target devices during domestic travel. FlowCloud utilizes DLL sideloading techniques to evade forensic analysis and communicates via legitimate cloud infrastructure to maintain covert persistence, executing keylogging, screen capture, file collection, and credential harvesting.

Meanwhile, Titan Panda has been active since at least 2021, focusing heavily on North American legal firms. By exploiting a hard-coded Internet Information Services (IIS) machine key vulnerability in Intapp Time Server software, Titan Panda achieved remote code execution across law firm networks. Once inside, the group deployed an in-memory framework designated IceGiant to execute long-term reconnaissance, persistence, and data exfiltration without triggering conventional file-based security alerts.
Implications for Global Cybersecurity
The deployment of framework-level artificial intelligence tools like ARTEX by state-sponsored actors marks a definitive turning point in cybersecurity history. Security analysts and industry experts emphasize that the primary implication is not necessarily the creation of novel attack vectors, but rather the radical acceleration of scale and efficiency.
By automating the tedious phases of vulnerability discovery, initial access, and internal reconnaissance, threat groups can cast a much wider net while maintaining operational stealth. This capability strains the defensive postures of traditional security operations centers (SOCs), which struggle to match the speed and parallel processing capacity of automated AI agents.
In response to the rapid proliferation of ARTEX across various cybercriminal and state-backed syndicates, industry leaders and software developers are calling for enhanced runtime monitoring, stricter controls over commercial LLM API usage, and advanced behavioral analysis frameworks capable of detecting automated, non-human interaction patterns within enterprise networks. As nation-state actors continue to refine agentic AI tools, the cybersecurity industry faces an escalating imperative to develop proactive, AI-driven defense mechanisms to protect critical global infrastructure.