Telegram Android Security Flaw Allows Malicious Widgets to Bypass Sandboxing and Execute Code

Recent cybersecurity disclosures have cast a spotlight on Telegram’s mobile infrastructure following the discovery of a significant architectural vulnerability within its Android application. Security researchers from NebuSec revealed that malicious interactive widgets—small, dynamic interface blocks driven by JavaScript sent via chat bots—can successfully bypass recently implemented security filters. This capability allows attackers to execute unauthorized code outside of the application’s intended sandbox environment.
The vulnerability directly impacts how Telegram isolates third-party executions on Android devices. While the platform attempted to mitigate early concerns by introducing process-level segregation and kernel-level monitoring, ongoing analysis indicates that these defenses remain incomplete, raising critical questions regarding application-level sandboxing, secure messaging architectures, and the inherent risks of extending dynamic script execution into chat interfaces.
Chronology of the Telegram Widget Security Incident
The unfolding security event began shortly after Telegram rolled out a feature enabling bots to transmit interactive widgets directly into chat messages. Designed to improve user engagement by rendering small web-like applications natively within conversations, these widgets rely on a lightweight JavaScript engine known as QuickJS. Because QuickJS processes run locally on the user’s mobile device, proper sandboxing is essential to prevent untrusted code from interacting with the underlying operating system.
Just two days after the feature debuted on Telegram’s live service—and while general-purpose bots were restricted on production servers—a security researcher operating under the handle V12 published a video demonstration on social media platform X. The demonstration claimed that arbitrary Telegram messages could be weaponized to execute remote code on targeted devices.
In response to the early reports, Telegram released version 13.2.2 (7303) of its Android application. The source code updates revealed that developers had isolated the QuickJS engine into a dedicated system process. Additionally, Telegram introduced a seccomp (secure computing mode) filter designed to restrict or log the system calls made by the QuickJS process.

However, NebuSec’s subsequent technical analysis demonstrated that these defenses could be circumvented. By leveraging unhandled widget bugs or chaining valid widget flaws with existing kernel vulnerabilities, researchers successfully forced the QuickJS engine to execute unauthorized commands, such as launching the native Android calculator app, entirely outside the bounds of the seccomp filter.
Technical Analysis: Breaking Down the Seccomp and Sandbox Failures
The core architecture of Telegram’s widget system relies on strict boundary enforcement, promising users that embedded code runs within an isolated environment devoid of network access or system-level privileges. According to official widget documentation, the QuickJS runtime is supposed to enforce these restrictions internally.
However, security analysts point out that memory corruption vulnerabilities—such as use-after-free conditions or out-of-bounds write errors within the QuickJS engine—fundamentally undermine these software-level guarantees. Once a script successfully achieves read and write primitives over the process memory, internal runtime restrictions fail, allowing attackers to manipulate the execution flow.
To counter this, Telegram deployed a seccomp filter atop Android’s native process limits. The filter was configured to monitor and restrict sensitive system operations, explicitly checking a few dozen system calls including ptrace, bpf, and mount. Despite these additions, technical inspection of the source code revealed notable gaps:
- Unfiltered System Calls: Critical system calls such as
ioctlwere left unfiltered, providing potential vectors for kernel-level interactions. - Shared Widget Processes: All widgets rendered within the application share a single, unified execution process. Consequently, if an attacker compromises a widget originating from one bot, the shared memory space exposes data across all active widgets within the session.
- Audit Mode Configuration: Source code inspections by third-party analysts like The Hacker News indicated that the seccomp filter within the published Android codebase was operating in an "audit" mode. Under this configuration, the system logs targeted calls and blocks process creation, but otherwise permits restricted system calls to execute unimpeded until stability logs confirm zero anomalous behavior.
Conflicting Official Statements and Active Exploitation
The vulnerability disclosures have triggered contrasting public statements from Telegram leadership and independent cybersecurity firms regarding the real-world risk to end-users.
Addressing early social media reports prior to the NebuSec demonstration, Telegram Chief Executive Pavel Durov firmly rejected claims of widespread, passive exploitation. In a public channel post, Durov stated that no user could be compromised simply by receiving a message. He emphasized that executing malicious code required deliberate user interaction, such as explicitly initializing a third-party service, and maintained that server-side mitigations had already neutralized the primary vectors identified in initial demonstrations.

Despite these assurances, independent telemetry from cybersecurity firm Kaspersky introduced a more alarming perspective. Kaspersky reported detecting active exploitation attempts targeting a vulnerability within Telegram widgets while users browsed specific public channels.
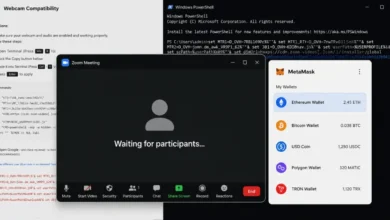
According to Kaspersky’s telemetry, the observed attacks involved the silent execution of a malicious PowerShell script. This script subsequently downloaded and deployed a payload identified as WebRAT (also known as Salat Stealer). The malware grants remote attackers comprehensive control over infected systems, specifically targeting sensitive user data including cryptographic wallet credentials and private Telegram account sessions. While Kaspersky’s warning did not explicitly link its telemetry to the V12 or NebuSec demonstrations or specify the exact software version exploited, the firm strongly advised users to disable or avoid interacting with Telegram widgets until comprehensive patches are widely deployed.
Broader Industry Implications and Outlook
The discovery of code execution vulnerabilities tied to Telegram’s widget infrastructure highlights the delicate balance modern messaging platforms must strike when expanding into feature-rich, application-like ecosystems. As chat applications evolve from simple text-and-media transmitters into decentralized platforms supporting mini-apps, bots, and dynamic widgets, their attack surfaces expand exponentially.
The incident underscores several crucial lessons for secure software development in consumer applications:
- Defense-in-Depth Limitations: Relying solely on sandbox engines like QuickJS is insufficient without robust, immutable operating system-level isolation. Memory corruption vulnerabilities within interpreters routinely bypass logical sandbox constraints.
- Strict Seccomp Configurations: Implementing monitoring filters in "audit mode" rather than enforcing strict blocking policies leaves operational windows open during critical rollout phases.
- Process Isolation: Sharing execution threads and memory spaces across disparate third-party bots magnifies the blast radius of a single compromised component, potentially exposing multi-tenant user data.
As of this writing, neither official public repositories nor NebuSec’s research notes have identified a finalized Common Vulnerabilities and Exposures (CVE) identifier or detailed a comprehensive, verified patch set addressing all vectors. Security analysts recommend that users exercise caution when engaging with third-party bots and monitor official Telegram update channels for forthcoming security advisories and application updates.