Navigating the Era of Mythos-Class Cyber Attacks: Why Traditional Vulnerability Management is Failing Modern Enterprises

The modern cybersecurity landscape is defined by an accelerating paradox: organizations possess more automated visibility into their software flaws than ever before, yet they remain dangerously exposed to rapid exploitation. When a new Common Vulnerabilities and Exposures (CVE) identifier is published, enterprise vulnerability scanners instantly flag the anomaly, frequently generating alarming severity scores based on standard metrics like the Common Vulnerability Scoring System (CVSS). However, a high severity score merely indicates the theoretical damage a flaw could inflict; it fails to answer the critical operational question that CISOs and security operations center (SOC) analysts must address: Can this specific vulnerability be successfully exploited within our unique production environment, configured with our specific compensating controls, network segmentation, and hardening policies?
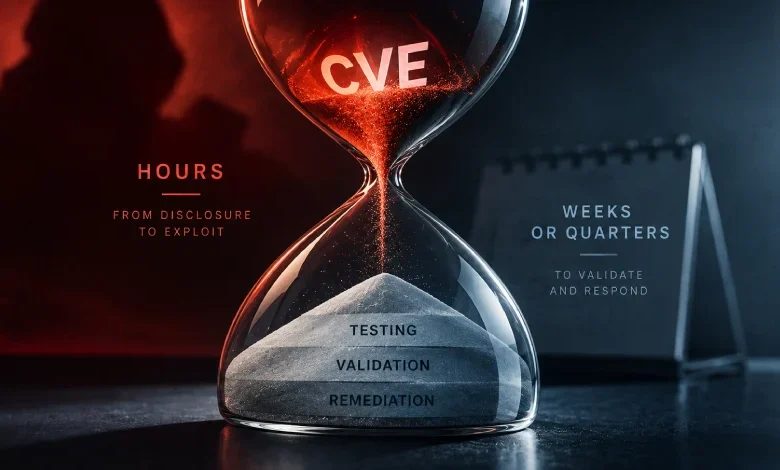
For decades, the standard cybersecurity cadence relied on weekly, monthly, or quarterly vulnerability assessment and penetration testing (VAPT) cycles. While this structured approach was arguably sufficient in an era of manual exploit development, it is fundamentally incompatible with the threat velocity of the mid-2020s. Today, the cybersecurity industry has entered the era of "Mythos-class" attacks—a paradigm shift heavily catalyzed by artificial intelligence and advanced automation. AI-driven threat actors are drastically compressing the critical timeline that spans from public vulnerability disclosure to the deployment of weaponized, working exploits. Consequently, the most dangerous vulnerability gap facing enterprises today is no longer strictly technical; it is temporal. While threat actors operate at machine speed, many defensive programs continue to validate risk on sluggish, human-driven timelines.
The Limitations of Severity-Based Prioritization
To understand why traditional vulnerability management is collapsing under its own weight, one must examine the fundamental flaw of prioritizing exclusively on severity metrics. A CVSS score of 9.8 or 10.0 creates an immediate panic across IT and security departments, often triggering emergency patching protocols for systems that may not even be exposed to the internet, or whose vulnerable code paths are blocked by upstream Web Application Firewalls (WAFs) and endpoint detection and response (EDR) solutions.
This reactive firefighting drains valuable technical resources, leads to patch fatigue, and frequently results in operational downtime when emergency updates destabilize production applications. Conversely, low- or medium-severity vulnerabilities—when chained together by sophisticated adversaries using automated attack paths—can lead to total domain compromise before security teams even finish triaging the initial alerts.
Security leaders are increasingly recognizing that prioritization must evolve from theoretical risk scoring to empirical threat validation. Knowing that a flaw exists is only the first step; proving whether it is exploitable under real-world conditions is what dictates true organizational resilience. This shift necessitates a continuous validation loop that tests security controls against known and emerging attack techniques immediately upon disclosure, rather than waiting for scheduled quarterly audits.
The Dilemma of Live Production Testing
Even when security teams recognize the necessity of validating vulnerabilities, they encounter a formidable operational obstacle: the inherent danger of executing live exploit code on production systems. Production environments are fragile ecosystems designed for uptime and business continuity, not for running aggressive exploit payloads that could crash databases, corrupt critical data pipelines, or introduce secondary security instabilities.
Because direct exploitation is often impractical or outright prohibited in live environments, organizations historically had to choose between flying blind—assuming their defensive controls would hold—or accepting the high risks associated with intrusive testing. Modern security architecture, however, offers a sophisticated middle ground through breach and attack simulation (BAS) and automated security validation platforms.

Rather than deploying raw, destructive exploit code against a live database, advanced validation frameworks allow defenders to map newly disclosed CVEs directly to specific adversary behaviors and attack techniques, such as those cataloged in the MITRE ATT&CK framework. Security teams can then safely emulate these behaviors against their actual security controls—testing whether firewalls drop the malicious traffic, whether intrusion detection systems (IDS) flag the anomalies, and whether endpoint agents intercept the subsequent process execution. This methodology provides concrete, evidence-based answers regarding control efficacy even when direct, destructive exploitation of the target asset is out of the question.
Bridging the Temporal Gap Between Defenders and Adversaries
The stark reality of modern threat intelligence is that adversaries are no longer constrained by the bureaucratic delays that plague corporate security departments. When a zero-day vulnerability or a critical patch disclosure hits the public domain, automated scanners deployed by cybercriminal syndicates and nation-state actors begin probing global IP space within minutes.
To counteract this asymmetry, security operations must fundamentally transform their validation workflows. If an enterprise’s underlying infrastructure, cloud configurations, and application stacks change within minutes via automated CI/CD pipelines, but its security validation cycle takes weeks or months, a catastrophic visibility vacuum is created. Closing this gap requires adopting continuous automated validation tools that integrate seamlessly with modern DevOps and DevSecOps pipelines.
Industry experts, including solutions architects specializing in automated security validation, emphasize that replacing outdated assumptions with defensible, data-driven answers is the only viable path forward. During upcoming industry forums, such as specialized technical webinars hosted by security leaders at firms like Picus, practitioners are increasingly focusing on practical workflows that transition teams away from static vulnerability lists toward dynamic, behavior-based readiness assessments. These sessions demonstrate how organizations can systematically verify their security posture against Mythos-class threats without compromising operational stability.
Broader Implications and the Future of Security Operations
The emergence of AI-driven, Mythos-class attack vectors signals a permanent transformation in how organizations must approach risk management. The traditional compliance-driven checkbox approach to vulnerability scanning is rapidly becoming obsolete, replaced by a demand for continuous, empirical proof of security posture.
Regulatory bodies and cyber insurance underwriters are also beginning to take notice of this shift. Increasingly, policies and compliance frameworks are favoring organizations that can demonstrate continuous control validation and rapid threat response over those that merely perform periodic vulnerability scans. Proof of exploitability and control efficacy is transitioning from a best practice to a fundamental prerequisite for corporate risk governance.
Ultimately, the challenge posed by accelerated attack timelines cannot be solved by working harder or hiring more analysts to manually sift through endless vulnerability alerts. It requires a structural evolution toward automated validation, where security teams continuously test, measure, and prove their readiness against real-world attack techniques. By aligning validation cadences with the speed of modern threat actors, enterprises can finally move ahead of the curve, ensuring that when the next major CVE drops, they possess not just an ugly severity score, but a definitive, validated answer regarding their operational safety.