The Evolving Threat of Evasion Techniques in Open-Source Ecosystems: Malicious NPM Packages and the Limits of Install-Time Scanning


The cybersecurity community has grown increasingly alarmed by a sophisticated wave of supply chain attacks targeting open-source software repositories, most notably the Node Package Manager (npm) registry. Recent analyses highlight an emerging class of malicious npm packages specifically engineered to bypass traditional install-time security scans. These evasive tactics underscore a profound shift in threat actor methodology, moving away from crude, easily detectable payload delivery toward nuanced, multi-stage execution models that blend seamlessly into normal development workflows. As organizations worldwide double down on software bill of materials (SBOM) generation and automated dependency checking, adversaries are adapting by weaponizing the very tools meant to ensure software integrity.
Background Context of the Open-Source Supply Chain Threat
Modern software development relies heavily on third-party libraries and packages to accelerate time-to-market. Ecosystems like npm, PyPI, and RubyGems host millions of components, allowing developers to assemble complex applications with minimal custom code. However, this modularity creates an expansive attack surface. Supply chain attacks—where adversaries inject malicious code into trusted software dependencies—have evolved from theoretical concerns to daily operational realities.
Historically, security tooling relied heavily on static analysis and signature matching executed during the installation phase of a package. When a developer or a CI/CD pipeline ran commands such as npm install, security scanners would inspect the package manifest, known vulnerabilities databases, and static file contents for known bad indicators. Recognizing this defensive posture, malicious actors began developing techniques to mask their intentions during installation. By deferring execution, obfuscating code logic, or verifying the runtime environment before payload deployment, attackers successfully slip past standard perimeter defenses.
Chronology of the Emerging Threat Landscape
The realization that install-time defenses are insufficient is not entirely new, but the sophistication of modern evasion strategies represents a distinct milestone in threat evolution. Over the past several years, researchers and security practitioners have documented a steady cadence of supply chain compromises.
In the early phases of repository security, malicious packages were often identified by obvious typosquatting or blatant inclusion of known malware strings, which static analyzers caught instantly. Attackers responded by introducing obfuscated JavaScript and splitting payloads across multiple seemingly innocuous files.
As detection engines grew smarter, incorporating heuristics and basic AST (Abstract Syntax Tree) parsing, threat actors transitioned to environmental awareness. Packages began checking whether they were running inside a sandbox, a CI/CD build runner, or a developer’s local machine. If an analysis environment was detected, the package would behave benignly, effectively hiding its malicious behavior from automated scanners. Only when deployed to a production environment or an unsuspecting target’s specific infrastructure would the payload execute.
Recent disclosures in late 2026 emphasize that this cat-and-mouse game has reached a tipping point. Analysts have cataloged campaigns where malicious npm modules utilize dynamic code loading, fetch remote payloads only after rigorous verification checks, and evade the static hooks typically monitored by repository maintainers.
Technical Analysis: Why Static Scans Fall Short
The fundamental limitation of install-time scanning lies in the nature of interpreted languages like JavaScript. JavaScript is inherently dynamic, supporting features like eval(), runtime code generation, and complex module loading mechanisms that can easily obscure the true intent of a script.
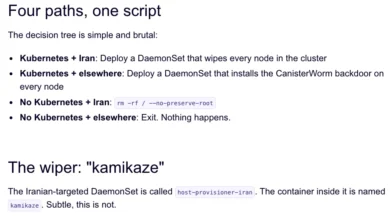
When a package is downloaded, static scanners evaluate the code at rest. However, a malicious package can remain completely dormant during installation. It may register a post-install script that does nothing more than download an encrypted resource from a remote command-and-control (C2) server, decrypt it in memory, and execute it without ever writing the malicious artifact to the local disk. Because the static files inspected by the registry scanner appear clean, the package passes automated vetting processes.
Furthermore, dependencies within modern software projects create a complex web of trust. A single application may depend on hundreds of direct and transitive packages. If a single low-level dependency is compromised, it inherits the trust granted to the entire application stack. Security analysts note that traditional dependency management tools struggle with this complexity, often lacking the contextual visibility required to distinguish between legitimate administrative tasks and unauthorized system modifications.
The Debate Over Client-Side Execution and Ecosystem Complexity
The proliferation of JavaScript across diverse environments—ranging from web browsers to server-side runtimes and operating system utilities—has long been a subject of intense debate among security architects and systems developers. Critics of ubiquitous script execution argue that forcing languages like JavaScript into contexts where they are unnecessary introduces massive, unmitigated attack surfaces.
Much like the legacy Flash player vulnerabilities of the past decade, client-side and runtime script execution models frequently become vectors for critical security flaws. Standards bodies and web committees face ongoing criticism for continuing to introduce features that allow remote code execution within client environments. While these features enable rich user experiences and developer convenience, they simultaneously complicate threat mitigation.
Concurrently, the open-source community grapples with systemic issues related to package maintenance, monolithic dependency trees, and corporate influence. Developers attempting to audit or minimize their software footprints often encounter a tangled nightmare of hard dependencies. Removing a seemingly extraneous utility package can inadvertently break critical system components due to rigid dependency coupling. This structural inflexibility leaves organizations vulnerable, as they are often forced to maintain software they neither fully understand nor truly need.
Industry Responses and Expert Recommendations
In response to these persistent supply chain vectors, cybersecurity authorities and industry experts have updated their guidance for software development lifecycle (SDLC) security. A consensus has emerged advising organizations not to rely solely on install-time or static scanning mechanisms.
Instead, security frameworks increasingly emphasize the necessity of runtime behavioral analysis. By monitoring application behavior in real-time—observing unexpected network outbound connections, unauthorized file system modifications, and anomalous process spawning—organizations can detect malicious activity regardless of how the payload entered the environment.
Security researchers advocate for the implementation of strict isolation boundaries, often conceptualized through sandbox environments, hypervisor-level monitoring, and containerization. Drawing parallels between traditional security paradigms, experts argue that "prison" environments—where processes operate under strict, probabilistic constraints and continuous behavioral observation—offer significantly better resilience than traditional perimeter "castle" defenses.
Moreover, software developers are urged to adopt stricter dependency pinning, internal registry mirrors, automated provenance verification (such as Sigstore and SLSA frameworks), and minimal privilege execution principles. By reducing the ambient authority granted to third-party packages, organizations can severely limit the potential blast radius of a compromised dependency.
Broader Impact and Future Implications
The ongoing evolution of evasive npm packages carries profound implications for the software industry at large. As nation-state actors, financially motivated cybercriminal syndicates, and sophisticated threat groups turn their attention toward open-source supply chains, the trust model underpinning modern software development faces an unprecedented stress test.
If developers and enterprises lose faith in the integrity of public repositories, the economic and operational efficiency afforded by open-source collaboration could be severely undermined. Conversely, the pressure to secure these ecosystems is driving rapid innovation in automated security tooling, runtime monitoring, and cryptographic software provenance tracking.
Ultimately, the defense against advanced supply chain attacks requires a fundamental shift in mindset. Organizations must transition from a reactive posture focused entirely on vulnerability patching and static artifact scanning to a proactive, defense-in-depth architecture centered on continuous runtime visibility, least-privilege execution, and rigorous behavioral analysis. Only through such comprehensive measures can the software development community hope to stay ahead of increasingly resourceful and evasive adversaries.
Related posts: