Bridging the Vulnerability Validation Gap in the Age of Mythos-Class AI Threats

The discovery of a new Common Vulnerabilities and Exposures (CVE) identifier routinely triggers a predictable cadence within enterprise security operations centers. Automated vulnerability scanners comb through corporate assets, flagging the latest software flaw, while standard metrics assign a severity score based on established frameworks like the Common Vulnerability Scoring System (CVSS). However, a high numerical severity rating frequently obscures the metric that holds true operational significance for defenders: whether the newly disclosed flaw can be successfully weaponized and exploited within a specific, localized enterprise environment.
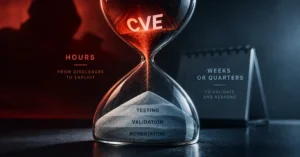
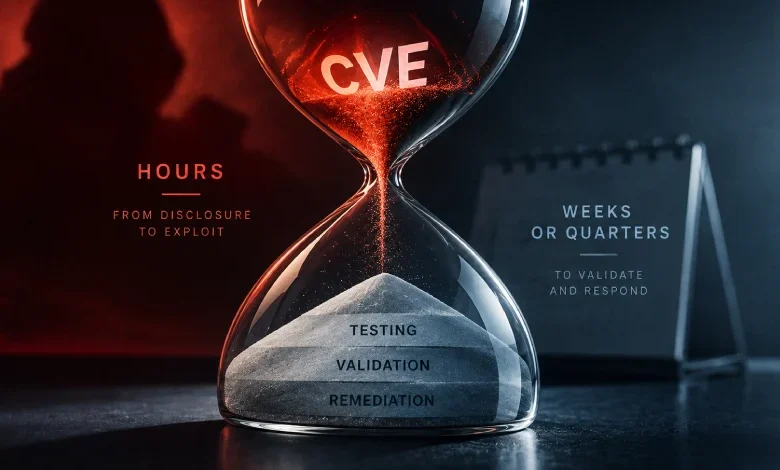
This fundamental disconnect between theoretical risk and contextual exploitability has been dangerously widened by the emergence of automated, AI-driven cyberattack capabilities. Described by industry analysts as Mythos-class threats, advanced artificial intelligence systems are radically compressing the timeline that exists between the initial public disclosure of a software vulnerability and the development of functional, reliable exploit code. While threat actors increasingly leverage generative intelligence and automated orchestration to accelerate their offensive operations, many corporate security programs remain anchored to legacy validation schedules, assessing organizational risk through static, manual reviews conducted on weekly, monthly, or quarterly cycles.
The resulting vulnerability validation gap is no longer strictly a technical hurdle; it is primarily a temporal crisis. Security teams are perpetually outpaced by adversaries who can iterate through attack vectors in a fraction of the time it takes an enterprise to verify its own defensive posture.
The Limitations of Severity-Based Prioritization
For decades, security operations teams have relied heavily on severity scores to triage remediation efforts. A critical severity rating—typically defined as a CVSS score of 9.0 or higher—frequently mandates immediate patching or emergency change management protocols. Yet, security experts have long argued that severity metrics evaluate inherent risk rather than contextual exposure.
A vulnerability may possess all the theoretical attributes required for remote code execution, but if the affected service is properly isolated behind robust network segmentation, restricted by web application firewalls, or executed under strict least-privilege principles, the practical risk drops significantly. Conversely, a medium-severity vulnerability residing on an exposed, mission-critical server with broad network access can present an immediate, catastrophic threat.
Relying solely on scanner output creates a false sense of security or, conversely, leads to alert fatigue. Security engineers are confronted with hundreds of high-severity alerts daily, forcing them to guess which findings represent genuine vectors of compromise. In an era where automated tooling enables threat actors to operationalize new vulnerabilities within hours of disclosure, guessing is no longer a viable defensive strategy. Organizations require empirical proof of exploitability tailored to their unique architectural topologies.
The Rise of Mythos-Class AI and Accelerated Exploitation Timelines
The cyber threat landscape has undergone a structural transformation driven by the maturation of artificial intelligence. Historically, the vulnerability lifecycle followed a well-documented timeline: researchers discovered a flaw, vendors coordinated a patch, and threat actors subsequently invested days or weeks in reverse-engineering the patch to develop reliable exploits.
The advent of automated reasoning and generative AI models capable of writing, testing, and refining exploit payloads has truncated this timeline to near-instantaneous execution. When a new CVE is published, advanced threat actor groups are increasingly positioned to deploy autonomous agents that analyze the patch diff, identify underlying logic flaws, and synthesize functional exploits before most enterprises have even completed their initial inventory scans.

This acceleration presents an asymmetric challenge. While defenders must verify patch applicability, test updates in staging environments, and schedule maintenance windows to avoid operational disruption, attackers face no such administrative friction. They operate continuously, leveraging automated infrastructure to scan for unpatched assets and execute multi-stage attacks. Consequently, the traditional vulnerability management lifecycle—characterized by periodic reporting and delayed remediation—is fundamentally misaligned with the velocity of modern offensive operations.
Evolving the Validation Loop: Moving Beyond Production Exploitation
One of the most persistent operational dilemmas facing security teams is the inherent danger of running active exploit code within live production environments. While penetration testing and red teaming provide valuable insights into organizational resilience, conducting live exploitation exercises against critical business infrastructure carries a tangible risk of service disruption, data corruption, or system crashes.
Because safe testing is paramount, many organizations hesitate to validate complex vulnerabilities, opting instead to rely on assumptions and vendor advisories. To resolve this tension, modern security validation frameworks are increasingly adopting threat emulation methodologies that decouple the proof of vulnerability from destructive live exploitation.
Instead of executing raw exploit payloads against production servers, advanced security platforms map newly disclosed CVEs directly to specific attack techniques, such as those cataloged in the MITRE ATT&CK framework. By simulating the behaviors, network traffic patterns, and execution mechanics associated with a given vulnerability against representative security controls, defenders can measure whether their endpoint detection and response (EDR) agents, security information and event management (SIEM) rules, and network firewalls would successfully block or detect the malicious activity.
This behavioral approach allows organizations to gather empirical evidence of their defensive posture without risking operational uptime. It replaces speculative risk assessments with concrete, data-driven answers while the vulnerability is still actively being weaponized in the wild.
Industry Response and Future Outlook
To address these escalating challenges, security architects and solution providers are emphasizing continuous threat exposure management (CTEM) as a necessary evolution of traditional vulnerability management. Frameworks that integrate automated breach and attack simulation (BAS) with real-time threat intelligence are gaining traction among enterprises seeking to close the validation gap.
Industry stakeholders, including technical specialists from security validation firms such as Picus Security, are actively demonstrating live workflows designed to transition organizations from reactive patch-tracking to proactive, continuous validation. Experts emphasize that the core objective of modern security operations is not merely to compile vulnerability lists, but to establish a defensible, continuous feedback loop between threat intelligence, control validation, and remediation prioritization.
As AI continues to reshape the methodologies of both attackers and defenders, the margin for error in enterprise security is narrowing. Organizations whose validation cycles operate on weeks or months will find themselves structurally disadvantaged against adversaries operating on a timescale of minutes. Bridging this gap requires a deliberate shift away from static metrics and a commitment to continuous, behavioral validation that proves control efficacy before an incident occurs.