Critical Unbound DNS Resolver Flaws Expose Infrastructure to Remote Code Execution Risks

NLnet Labs has released Unbound version 1.26.1 to address a series of severe vulnerabilities, most notably a critical heap overflow within the DNSSEC validator. Identified as CVE-2026-81642, this vulnerability affects every release of the popular open-source recursive DNS resolver prior to 1.26.1. If successfully exploited by an adversary operating a malicious authoritative name server, the flaw permits remote code execution (RCE) on vulnerable systems without requiring any user interaction or prior authentication.
The emergency patch release also mitigates eight additional security flaws, including a high-severity heap corruption vulnerability discovered by security researchers at Anthropic. As network administrators scramble to deploy updates, cybersecurity agencies and maintainers alike emphasize the urgent need for patching to protect global internet infrastructure against potential denial-of-service (DoS) conditions and systemic compromises.
Anatomy of the Critical DNSSEC Validator Flaw
The most severe issue resolved in the 1.26.1 update, tracked as CVE-2026-81642, carries a maintainer-assigned CVSS severity score of 9.1 out of 10, categorizing it as critical. According to technical advisories published by NLnet Labs, the vulnerability originates within the DNSSEC (Domain Name System Security Extensions) validator component of the Unbound resolver.
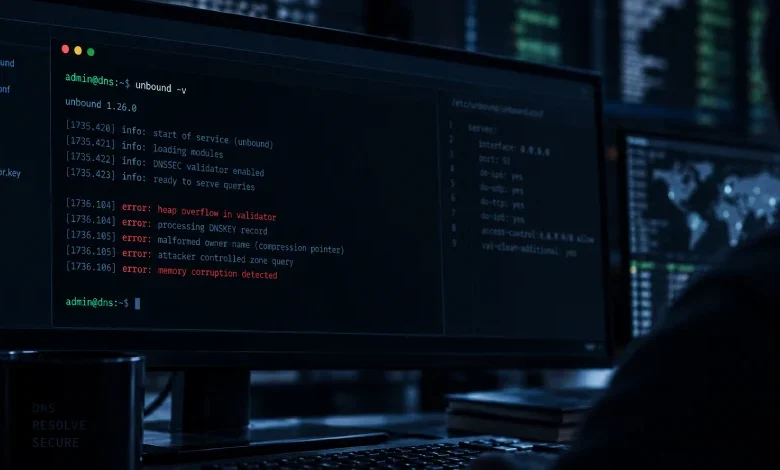
Specifically, the heap overflow occurs when the validator parses and digests a specially crafted DNSKEY record. In this attack scenario, the owner name of the DNSKEY record is engineered to act as a compression pointer pointing directly into the record’s own payload data. When the vulnerable software processes this malformed pointer, it fails to handle memory boundaries correctly, resulting in a heap overflow.
While the primary immediate impact cited by the maintainers is a denial of service—manifesting as resolver crashes or service unavailability—the flaw can potentially be leveraged by sophisticated attackers to achieve remote code execution. Because the network attack vector requires zero privileges and no user interaction, an attacker who successfully coaxes a vulnerable resolver into querying a malicious zone can execute arbitrary code under the security context of the Unbound process.
Scope of Vulnerability and Additional High-Severity Bugs

The patch covers all iterations of Unbound up to and including version 1.26.0. This extensive affected range includes recent security updates such as version 1.25.2, released in July, and version 1.26.0, deployed in early August. Maintainers have clarified that this vulnerability is distinct from CVE-2026-33278, a separate critical validator flaw patched earlier in the year via version 1.25.1.
In addition to CVE-2026-81642, the 1.26.1 patch bundle remediates eight other vulnerabilities of varying severity levels. Among these is CVE-2026-82717, a high-severity heap corruption bug located in the CNAME synthesis code path. Reported by Ben Morris of artificial intelligence firm Anthropic, this flaw can likewise result in remote code execution under specific operating system architectures and compiler configurations.
Another notable inclusion is CVE-2026-81634, a high-severity issue triggered when processing maximum-length (255-character) query names paired with exceptionally large TCP responses sourced from compromised or malicious name servers. This condition reliably triggers a denial of service.
The remaining fixes target medium- and low-severity vulnerabilities affecting specific features and operational configurations. For instance, CVE-2026-77955 affects zones utilizing "zonemd-check" parameters, while CVE-2026-78227 and CVE-2026-82720 involve denial-of-service vectors tied to QUIC and HTTPS transport protocols when built with specific library flags like --with-libngtcp2 and --with-libnghttp2. Furthermore, CVE-2026-85501 addresses algorithmic complexity attacks known collectively as ReTrap (including TagTrap, DelegationTrap, NsecTrap, and AdditionalTrap), prompting a default configuration change where val-clean-additional is now disabled by default to prevent unnecessary DNSSEC validation on additional data sections.
Chronology and Responsible Disclosure
The discovery and remediation timeline for the primary vulnerability highlights a streamlined coordination effort between independent security researchers and open-source maintainers. The core issue tracked as CVE-2026-81642 was formally reported to NLnet Labs on August 11, 2026, by Yuqi Qiu and Xiang Li from the AOSP Lab at Nankai University.
Demonstrating rapid response protocols, NLnet Labs developed a functional security patch by the following day, August 12. After a period of validation and testing by the original reporters, the patch was verified on August 13. Following standard coordinated vulnerability disclosure practices for non-public issues, NLnet Labs consolidated the fix alongside its routine maintenance schedule, officially publishing Unbound 1.26.1 approximately five weeks later on September 17, 2026.
As of the initial disclosure, neither NLnet Labs nor the Cybersecurity and Infrastructure Security Agency (CISA) had recorded any active exploitation of CVE-2026-81642 in the wild. CISA’s tracking portal designated the exploitation status as "none" upon publication, providing a critical window of opportunity for system administrators to upgrade before threat actors weaponize the publicly available patches.

Mitigation, Patching Procedures, and Debian Ecosystem Impact
Given the severe nature of the vulnerabilities and the potential for remote code execution, system administrators managing recursive DNS infrastructures are strongly advised to upgrade to Unbound 1.26.1 immediately. The updated release package is available via the official NLnet Labs download portal as source code—complete with cryptographic PGP signatures and checksums—alongside pre-compiled Windows binaries and installers.
For environments where immediate binary upgrades are operationally challenging, NLnet Labs has provided localized source patches designed to integrate cleanly into version 1.26.0 codebases. However, the maintainers reiterate their formal security policy, which prioritizes patching the latest stable software branch.
Downstream Linux distributions have begun incorporating the updates into their respective security trackers. Notably, the Debian security tracker announced that version 1.26.1-1 had been successfully integrated into the unstable branch. Meanwhile, widely deployed stable distributions—including Bookworm, Trixie, and Forky—remained flagged as vulnerable pending package maintainer backports and repository updates.
Broader Implications for Enterprise and ISP DNS Architecture
The discovery of critical vulnerabilities in foundational DNS software such as Unbound underscores the enduring fragility of core internet routing and resolution components. Because recursive resolvers sit at the boundary between enterprise networks, Internet Service Providers (ISPs), and the global Domain Name System, a compromised resolver can expose vast pools of users to advanced cache poisoning, traffic redirection, and internal network reconnaissance.
The inclusion of multiple denial-of-service vectors—ranging from algorithmic complexity attacks to resource exhaustion via persistent Transmission Control Protocol (TCP) and DNS-over-TLS (DoT) connections—highlights an evolving threat landscape where attackers target both the memory safety and the computational efficiency of network daemons.
Security analysts stress that organizations operating public-facing or internal recursive resolvers must adopt proactive vulnerability management frameworks. Relying solely on perimeter defenses is insufficient when vulnerabilities reside deep within packet parsing and cryptographic validation engines. By updating to Unbound 1.26.1 and auditing resolver configurations, network operators can mitigate the risk of catastrophic system compromise and maintain the integrity and availability of enterprise naming services.