High-Severity Vulnerability in Elementor Plugin Exposes Over Two Million WordPress Sites to Complete Takeover

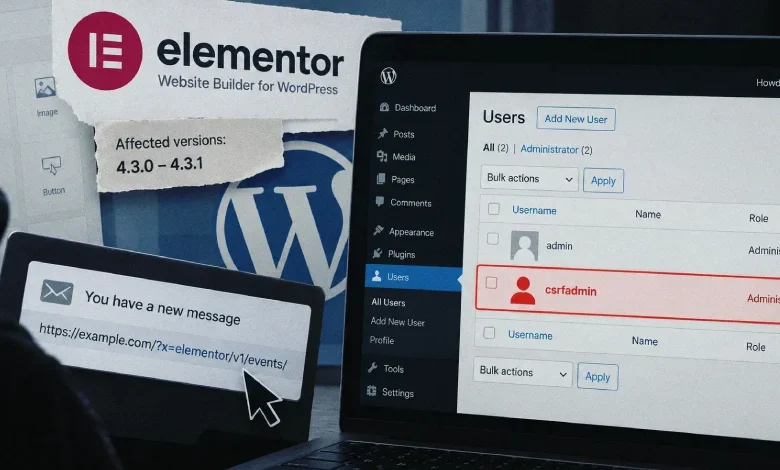
Website security researchers have disclosed a critical high-severity security vulnerability affecting the widely used Elementor Website Builder WordPress plugin. The flaw, categorized as a cross-site request forgery (CSRF) vulnerability, carries a severe CVSS score of 8.8 out of 10.0 and allows unauthenticated threat actors to forge malicious requests capable of creating rogue administrator accounts. Consequently, malicious operators could achieve complete administrative control over vulnerable WordPress installations simply by tricking a site administrator into clicking a specially crafted hyperlink.
The discovery highlights the ongoing challenges of maintaining robust security postures within the sprawling WordPress ecosystem, where third-party plugins serve as both functional powerhouses and potential entry points for malicious exploitation. Because Elementor commands a massive market presence across millions of active domains, security operations centers and independent web administrators have treated the disclosure with immediate urgency, pushing patches across affected infrastructures to mitigate the risk of widespread, automated attacks.
Scope of Vulnerability and Affected Versions
The security flaw is specifically confined to versions 4.3.0 and 4.3.1 of the Elementor Website Builder plugin. According to official telemetry and download statistics provided by WordPress.org, Elementor as a whole is active on more than 10 million live websites, making it one of the most deployed tools in the entire content management system ecosystem. While earlier and later iterations of the software remain unaffected by this specific bug, the two compromised versions alone were installed on more than 2 million active websites prior to the release of an emergency security update.
The restricted version range is due to the recent introduction of the Editor Events module, which debuted in version 4.3.0. Because legacy versions of Elementor prior to 4.3.0 do not feature this specific module or its accompanying proxy mechanism, they entirely lack the code path responsible for the vulnerability. Nevertheless, the sheer volume of sites that rapidly adopted versions 4.3.0 and 4.3.1 meant that millions of web properties faced an immediate and critical exposure window.
Technical Breakdown of the CSRF Bypass
The root cause of the vulnerability lies within the way the Elementor plugin handles cookie-authenticated REST API requests inside its newly implemented Editor Events module. Security analysis conducted by WordPress security firm Patchstack revealed that the module intentionally skips crucial cross-site request forgery protection mechanisms whenever the literal string elementor/v1/events/ appears anywhere inside the incoming request Uniform Resource Identifier (URI).
In standard web architectures, the request URI encompasses not only the path of the endpoint but also the accompanying query string parameters. Because external threat actors have full control over the composition of links they distribute via phishing emails, instant messaging platforms, or public comment sections, they can easily append custom query parameters to manipulate the URI structure. By appending a harmless-looking query parameter containing the required substring—such as x=elementor/v1/events/—an attacker can trick the server into entirely bypassing CSRF verification for that specific request.
What makes this vulnerability particularly dangerous is that the protection bypass does not merely apply to Elementor’s internal routing; it inadvertently exposes the entire REST API surface of the affected WordPress site. This means the flaw compromises WordPress core routes as well as the custom routes of every other installed plugin and theme on the target server. An unauthenticated attacker can leverage this bypass against core administrative endpoints, such as the /wp/v2/users route, executing a cross-site request forgery payload designed to silently register a brand-new administrator account.
An attack vector of this nature does not require complex technical prerequisites or sophisticated multi-stage exploitation frameworks. The malicious link does not need to rely on executing arbitrary JavaScript, submitting an interactive form, or luring a target to a malicious web page controlled by the threat actor. Instead, a simple anchor tag embedded in a standard plain-text email, a corporate chat message, or a forum post is entirely sufficient. If a logged-in WordPress user—particularly an administrator—clicks the link, the browser automatically attaches the necessary authentication cookies, forcing the user’s account to execute the unauthorized REST API action in the background without their knowledge or consent.

Chronology and Responsible Disclosure
The timeline of the vulnerability’s discovery, disclosure, and remediation unfolded rapidly through coordinated vulnerability reporting channels. A security researcher operating under the online pseudonym "Saggre" originally discovered the flaw during routine security auditing of the Elementor plugin’s codebase. Recognizing the severe implications of an unauthenticated administrative privilege escalation vector, the researcher initiated responsible disclosure practices, notifying the vendor and relevant security stakeholders so that a secure patch could be developed and deployed before public details emerged.
Following the receipt of the vulnerability report, Elementor’s engineering team engineered a security patch designed to correct the flawed URI validation logic within the Editor Events module. The fix was officially incorporated into version 4.3.2 of the plugin, which was released to the public earlier in the week. Independent security vendors subsequently published detailed technical advisories warning administrators of the active threat and urging immediate updates. Because the advisory details and proof-of-concept request structures have now entered the public domain, cybersecurity analysts emphasize that any lingering unpatched sites face an aggressively elevated risk of automated scanning and exploitation by opportunistic threat actors.
Mitigation and Remediation Guidelines
In response to the disclosure, website administrators running the Elementor plugin have been strongly urged to verify their current version numbers immediately. Sites utilizing versions 4.3.0 or 4.3.1 must apply the update to version 4.3.2 or any subsequent secure release without delay. Given the zero-interaction nature of CSRF attacks involving logged-in users, relying solely on perimeter defenses or waiting for scheduled maintenance cycles leaves organizations dangerously exposed.
Security best practices for WordPress administrators in the wake of this incident extend beyond simply updating the vulnerable plugin. Webmasters are advised to conduct immediate forensic audits of their user database to check for unauthorized or unfamiliar administrator accounts. Routine audits of user roles and capabilities help ensure that rogue profiles created during an active exploitation window can be identified and purged before malicious code execution or data exfiltration occurs.
Furthermore, security experts recommend implementing defense-in-depth measures across all WordPress installations. Enforcing strict multi-factor authentication (MFA) for all administrative and editor-level accounts adds a critical layer of defense, as even if a threat actor successfully exploits a CSRF flaw to trigger a REST API request, additional authentication challenges can prevent unauthorized session hijacking or privilege escalation. Utilizing robust web application firewalls (WAFs) and security plugins capable of monitoring unauthorized REST API abuse and anomalous user creation attempts provides an additional safety net against emerging web application vulnerabilities.
Broader Implications for the WordPress Ecosystem
The Elementor incident underscores a recurring structural risk inherent in modern content management systems and plugin-driven architectures. As plugins grow in complexity and integrate deeper into core application layers—such as REST APIs, asynchronous event handlers, and background proxy modules—the attack surface expands exponentially. A single logic flaw or oversight in URI parsing within a popular plugin can inadvertently compromise the security integrity of the entire CMS core and every other installed component.
With millions of websites relying on third-party software vendors for daily functionality, supply chain security and rigorous internal code reviews remain paramount. The rapid response by the Elementor development team and the swift advisory publication by independent security watchdogs like Patchstack demonstrate the effectiveness of the cybersecurity research community’s coordinated disclosure framework. However, the ultimate responsibility for defense rests with individual site operators, who must maintain vigilant patch management routines to safeguard digital assets against evolving web threats.
Related posts: