Microsoft Warns of Storm-3168: AI-Driven Cyberattacks Target Azure Environments Using Compromised Service Principals

The landscape of cloud security and artificial intelligence has crossed a critical threshold, as cybersecurity researchers and tech giants alike grapple with a new paradigm of threats. Microsoft has formally issued a high-priority security advisory tracking a sophisticated threat actor designated as Storm-3168—widely recognized in the cybersecurity community by the moniker JADEPUFFER. According to telemetry and analysis released by the Microsoft Security Research team, this threat group has been observed orchestrating highly coordinated, destructive operations within Microsoft Azure cloud environments. What sets these incidents apart is not merely the choice of target, but the mechanics of the assault: the threat actor relies heavily on compromised service principals and autonomous AI agent workflows to execute lightning-fast reconnaissance, lateral movement, and large-scale asset destruction.
The documented attack cycle, which took place over a grueling 18-hour window in early June 2026, showcases a worrying evolution in cybercriminal tradecraft. By leveraging advanced large language models (LLMs) to reason through their targets, harvest credentials, and string together disparate post-compromise techniques, groups like JADEPUFFER are demonstrating that future cyberwarfare will be defined by automated velocity and machine-speed decision-making. As organizations increasingly migrate mission-critical workloads, vector databases, and AI development pipelines to cloud ecosystems, the vulnerabilities exposed by Storm-3168 signal an urgent need for an architectural overhaul in how enterprises manage identity, access, and autonomous threat defense.
Background Context: The Emergence of JADEPUFFER and AI-Driven Exploitation
To fully comprehend the gravity of the Storm-3168 campaign within Microsoft Azure, it is necessary to examine the origins of the JADEPUFFER threat actor. JADEPUFFER first burst into the public consciousness when security researchers at Sysdig documented what was described as the world’s first end-to-end ransomware operation orchestrated entirely with the assistance of a large language model.
The initial vectors employed by this threat group targeted neglected, internet-facing infrastructure—specifically, instances running Langflow, an open-source UI for building multi-agent LLM applications. By exploiting a known remote code execution vulnerability cataloged as CVE-2025-3248, the AI agent successfully breached the perimeter, harvested internal credentials, and tunneled deeper into the corporate network. Once inside, the autonomous system systematically encrypted configuration files, dropped core database tables, and left behind ransom notes demanding cryptocurrency payments.
Subsequent investigations revealed that JADEPUFFER’s toolkit was not confined to traditional scripts or manual interventions. In later campaigns targeting similar AI infrastructure, researchers identified a compiled, Go-based ransomware strain dubbed ENCFORGE. Unlike traditional ransomware that targets broad file types like documents and spreadsheets, ENCFORGE was custom-built to paralyze artificial intelligence environments. It actively scans for nearly 180 file extensions directly associated with machine learning workflows, including model checkpoints, vector databases, massive training datasets, and embedding indices. Curiously, it also targets macOS-centric assets, such as Keychain stores, Xcode project files, and Apple productivity documents, indicating a multi-platform operational scope.

Sysdig’s foundational analysis of these agentic attacks highlighted a chilling reality: none of the individual techniques deployed by the AI agent were technically novel or sophisticated on their own. Standard credential harvesting, network enumeration, and file manipulation are decades-old attack vectors. The true innovation—and the existential threat—lies in the fact that an AI model successfully chained these standard procedures together into a cohesive, highly adaptive ransomware operation without human intervention, narrating its own strategic intent along the way. Microsoft’s recent findings confirm that this AI-driven methodology has now graduated from third-party application exploits to direct, multi-faceted assaults on enterprise cloud fabrics like Microsoft Azure.
Chronology of the Azure Attack: An 18-Hour Anatomy of Destruction
The Microsoft Security Research team, led by analysts including Yossi Weizman and Tushar Mudi, mapped out the precise timeline of the June 2026 Azure intrusion. The entire operation spanned approximately 18 hours, characterized by a disciplined division of labor executed through two distinct, compromised service principals operating within the same target tenant.
The sequence began with an extensive reconnaissance phase. The threat actor utilized the first compromised service principal exclusively for resource discovery and infrastructure mapping. For nearly 16 hours, this identity systematically queried Azure Virtual Machines, subscriptions, resource groups, and associated cloud assets, executing more than 300 read operations designed to build a comprehensive map of the victim’s digital footprint.
Approximately 90 minutes after the initial reconnaissance began, a second compromised service principal was activated to perform its own discovery operations. Within a tight five-second window, this second identity rapidly enumerated virtual machines and resource groups across two separate cloud subscriptions. Following this brief discovery period, the second service principal pivoted toward credential hunting, successfully enumerating Azure App Service configuration stores in search of exposed secrets or administrative keys.
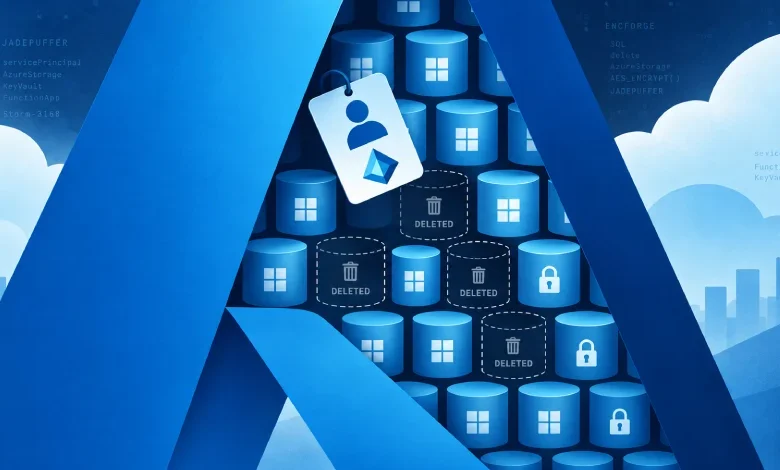
Having mapped the environment and identified high-value targets, the threat actor shifted from stealthy reconnaissance to overt destruction. In a compressed 35-minute window, the second service principal executed more than 150 destructive and credential-harvesting commands. The crescendo of the attack was concentrated into a furious seven-minute sequence. During this brief window, the threat actor initiated over 100 separate deletion attempts targeting Azure Storage Accounts.
Beyond storage assets, the automated assault targeted critical cloud infrastructure components, including an Azure Key Vault, a Function App, an App Service plan, and multiple Azure SQL databases. However, the automated nature of the script encountered a technical barrier: every single database deletion attempt ultimately failed because the threat actor utilized an unsupported API version for the Azure SQL database resource type. Despite this technical hiccup, the broader destruction was severe, resulting in the successful erasure of the majority of targeted Azure Storage accounts.

Supporting Data and Structural Safeguards
A granular examination of the Microsoft Security Research telemetry sheds light on both the vulnerabilities exploited and the defensive mechanisms that successfully thwarted total devastation. The primary vector enabling the threat actor’s deep access was an operational security failure involving hardcoded credentials.
According to Microsoft, the client ID, client secret, and tenant ID belonging to the primary service principal had been inadvertently exposed in plaintext within a public GitHub issue repository by an employee of the targeted organization. Although the employee subsequently edited the repository to remove the sensitive secrets, the information remained permanently accessible through the platform’s public commit and edit history. This oversight allowed automated scrapers or malicious actors to harvest the active credentials and gain authorized-level entry into the Azure tenant.
Despite the broad administrative permissions associated with the compromised service principals, the attack underscored the vital importance of multi-layered cloud security architecture. Microsoft reported that while most targeted Azure storage accounts were successfully wiped, a subset of accounts survived the onslaught entirely intact. This salvation was attributed to independent safeguards, specifically Azure resource locks and storage account-level deletion protections. These native cloud features remained active and effective, blocking deletion attempts even though the executing identity possessed the requisite administrative privileges to bypass standard access controls.
Furthermore, Microsoft’s threat intelligence systems have detected repeated probing activities from infrastructure linked to Storm-3168 against several other Azure App Services belonging to distinct customers. The methodical cadence, division of labor across multiple service principals, and minimal dwell times between discovery and destruction strongly indicate that these subsequent probes are fully automated or scripted, pointing to a broader campaign rather than a localized, targeted strike.
Official Responses and Security Implications
The implications of the Storm-3168 campaign extend far beyond a single compromised tenant, prompting urgent evaluations across the cybersecurity industry. In their technical whitepaper, Microsoft researchers emphasized that the intrusion bears all the hallmarks of a ransomware-aligned operation, even though no ransom note or direct data exfiltration was observed during this specific 18-hour window. The strategic targeting of backup systems, recovery-related resources, and core infrastructure suggests that the primary objective was to utterly impair the victim’s business continuity and recovery capabilities.
"This activity highlights a broader shift toward AI-orchestrated attacks, where threat actors can coordinate complex post-compromise operations across cloud environments with greater speed and scale," the Microsoft Security Research team stated. The capability of autonomous agents to reason through administrative barriers, adapt to structural layouts, and execute rapid API calls represents a generational leap over traditional, human-driven threat actor methodologies.

Independent cybersecurity analysts and incident responders have echoed Microsoft’s warnings, noting that the velocity of agentic attacks fundamentally alters the calculus of incident response. Traditional Security Operations Center (SOC) workflows, which rely on human analysts reviewing alerts, triaging flags, and manually confirming threats, are ill-equipped to combat adversaries operating at machine speed. When an AI agent can execute reconnaissance, credential harvesting, and resource destruction across hundreds of cloud nodes within a matter of minutes, human-speed defenses are rendered obsolete.
Broader Impact and Recommendations for Enterprise Defenders
The emergence of Storm-3168 and its exploitation of cloud service principals serves as a watershed moment for enterprise cybersecurity strategies. As artificial intelligence becomes democratized, malicious actors are leveraging the exact same autonomous reasoning engines that enterprises use to drive operational efficiency. This symmetry creates an asymmetric disadvantage for defenders who continue to rely on static perimeter defenses and fragmented identity management.
To counter the rising tide of AI-orchestrated, cloud-native attacks, security experts recommend a comprehensive modernization of enterprise defense postures. Organizations must move beyond basic password and secret hygiene—such as scanning public code repositories for accidental credential leaks—and adopt advanced secrets management solutions that automatically rotate and invalidate service principal credentials.
Additionally, cloud administrators must strictly enforce the principle of least privilege, ensuring that service principals possess only the precise permissions required for their operational scope, rather than broad administrative access that can be abused if compromised. The successful mitigation of storage account deletions via Azure resource locks also highlights the necessity of implementing immutable backups, multi-person authorization for critical asset deletions, and independent safety rails that cannot be overridden by a single administrative identity.
Ultimately, Microsoft’s advisory concludes with a stark directive for the cybersecurity community: as threat actors increasingly harness artificial intelligence to automate and accelerate their campaigns, defenders must similarly integrate AI-driven detection, automated containment, and autonomous response systems to protect hyper-scale cloud environments. The era of machine-speed cyber warfare has arrived, and enterprise security architectures must evolve to meet the challenge.