CISA Adds Active Exploits in JFrog, ConnectWise, and MikroTik to Known Exploited Vulnerabilities Catalog

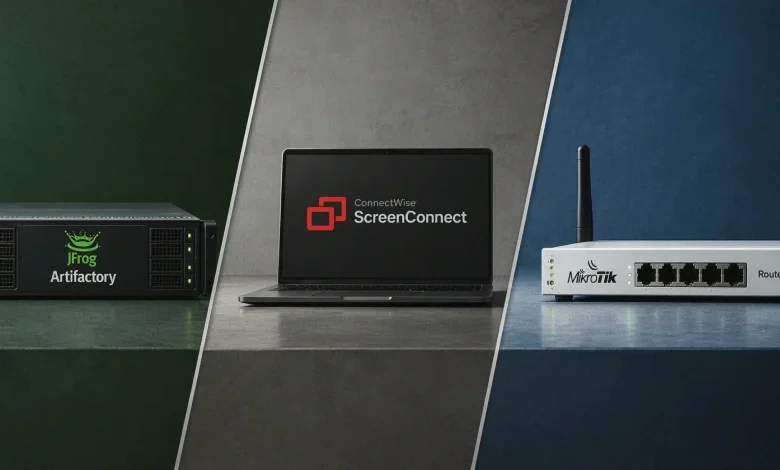
The United States Cybersecurity and Infrastructure Security Agency (CISA) has expanded its influential Known Exploited Vulnerabilities (KEV) catalog to include five critical security flaws affecting enterprise staples, including JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik RouterOS. The agency’s directive mandates that Federal Civilian Executive Branch (FCEB) agencies apply the corresponding security patches within strict compliance windows, emphasizing the escalating urgency driven by active exploitation in the wild.
These additions underscore a broader, troubling trend in contemporary cyberattacks: threat actors increasingly rely on complex exploit chains targeting enterprise development infrastructure, remote management tools, and core networking hardware. Security researchers from cloud-security firm Wiz, managed detection and response provider Huntress, and European incident response authorities have all contributed telemetry mapping the active campaigns exploiting these vulnerabilities, prompting swift regulatory action from U.S. cyber defenders.
Anatomy of the Attacks: JFrog Artifactory Chaining and Persistence
The most complex and damaging campaign highlighted by recent threat intelligence reports involves active exploitation of self-hosted JFrog Artifactory instances. Between August 15 and September 8, malicious actors were observed weaponizing a combination of software vulnerabilities to bypass authentication frameworks, escalate user privileges, and ultimately seize full administrative control over unpatched enterprise servers.
The attack vector heavily relies on chaining vulnerabilities, most notably tying multiple Artifactory bugs to a critical remote code execution flaw designated as CVE-2026-82329, which carries a maximum CVSS severity score of 9.8. This specific vulnerability was initially incorporated into CISA’s KEV catalog earlier in the month, but subsequent intelligence indicates that threat actors are systematically bundling it with additional zero-day or recently disclosed flaws.
According to cloud security posture management firm Wiz, the post-exploitation lifecycle observed in these intrusions follows a predictable yet highly resilient pattern. Once threat actors breach an Artifactory server through the exploit chain, they immediately establish persistence by creating unauthorized administrator accounts. Following account creation, the attackers deploy malicious Groovy plugins designed to execute arbitrary code within the Java-based environment. Finally, they install custom, Rust-based backdoors, ensuring long-term access to the internal software supply chain environment even if superficial perimeter defenses are repaired.
Because JFrog Artifactory is frequently deployed as a central repository for proprietary source code, software binaries, and enterprise dependencies, a successful compromise of these servers grants malicious entities deep visibility into and potential tampering rights over an organization’s software development lifecycle (SDLC). This positions the vulnerability chain not merely as an infrastructure threat, but as a dangerous vector for upstream supply chain contamination.
Remote Management Risk: ConnectWise ScreenConnect Exploits
Parallel to the software repository attacks, CISA added a critical vulnerability affecting the ConnectWise ScreenConnect client, tracked as CVE-2026-84869, to the KEV catalog. Unlike server-side vulnerabilities that expose backend infrastructure, this flaw centers on client-side behavior during active remote support sessions.
Security investigations conducted by Huntress brought this activity to light, documenting at least three distinct incidents where malicious actors manipulated rogue ScreenConnect clients to push malicious Visual Basic Script (VBScript) payloads onto newly connected host systems.
ConnectWise formally categorized the issue as a specific condition within the ScreenConnect client software that permits files to be transferred and subsequently executed across an active remote session without requiring explicit authorization or confirmation from the host user under certain operational circumstances. Crucially, ConnectWise emphasized that the core ScreenConnect servers remain unimpacted by this vulnerability, limiting the attack surface to client-side installations.

In their technical breakdown, Huntress analysts warned that the flaw could be weaponized during legitimate-looking support or management sessions to silently drop secondary payloads onto unsuspecting client systems, including leveraging elevated execution actions. To mitigate this exposure, software vendor ConnectWise released version 26.6.5, urging all commercial users and managed service providers (MSPs) to update their client deployments immediately.
Network Infrastructure Compromise: The "MikroTrick" RouterOS Campaign
Rounding out CISA’s latest KEV additions are two security flaws impacting MikroTik RouterOS devices, tracked as CVE-2026-67277 and CVE-2026-86060. The inclusion of these network infrastructure bugs follows a comprehensive threat intelligence advisory published by CERT Polska, which detailed coordinated attacks against internet-facing routers.
According to CERT Polska, unknown threat actors successfully exploited these two RouterOS vulnerabilities in tandem, creating an attack chain that security analysts dubbed "MikroTrick." This exploit methodology allows malicious operators to bypass authentication mechanisms entirely and achieve complete administrative takeover of vulnerable MikroTik routing hardware.
Because routers sit at the perimeter of enterprise networks, taking administrative control of a gateway device grants attackers unprecedented visibility into network traffic, the ability to intercept sensitive communications, and a stable pivot point for lateral movement deeper into corporate or government networks. The exploitation of MikroTik infrastructure highlights the enduring vulnerability of edge devices, which frequently lack advanced endpoint detection and response (EDR) agents and may suffer from lax patch management protocols compared to traditional server infrastructure.
Regulatory Timelines and FCEB Compliance Deadlines
Under the legal authority granted by the Cybersecurity Act of 2015 and reinforced through binding operational directives, CISA imposes strict remediation timelines for Federal Civilian Executive Branch agencies whenever vulnerabilities are added to the KEV catalog. While these directives technically apply only to federal civilian agencies, the private sector widely regards CISA’s deadlines as critical benchmarks for enterprise risk management.
The mandatory patching windows for the latest batch of vulnerabilities are segmented based on perceived operational risk:
- MikroTik RouterOS Flaws (CVE-2026-67277, CVE-2026-86060): Must be remediated by FCEB agencies no later than September 13, 2026.
- ConnectWise ScreenConnect Flaw (CVE-2026-84869): Must be remediated by September 14, 2026.
- JFrog Artifactory Flaws: Must be remediated by September 25, 2026.
These compressed timeframes reflect the high velocity of active exploitation observed by commercial threat intelligence partners. Cybersecurity agencies globally continue to urge private enterprise organizations, critical infrastructure operators, and managed service providers to mirror these compliance deadlines to prevent wide-scale operational disruptions.
Broader Implications for Enterprise Security
The simultaneous escalation of threats across disparate technology categories—software development repositories, remote management utilities, and network routing hardware—highlights the multifaceted nature of modern cyber threats. Attackers are no longer reliant on a single class of vulnerability; instead, they aggressively combine software supply chain weaknesses, client-side trust abuse, and perimeter gateway flaws to achieve their strategic objectives.
Security analysts emphasize that traditional perimeter security models are insufficient for addressing vulnerabilities like those found in JFrog Artifactory and ConnectWise ScreenConnect. Because these tools inherently require a degree of trust and internal network connectivity, successful exploits can bypass conventional firewalls.
Organizations are advised to prioritize automated vulnerability scanning, implement strict principle-of-least-privilege access controls for administrative accounts, monitor for anomalous out-of-band network traffic originating from development servers and routers, and maintain robust, offline backups of software repositories to safeguard against persistent backdoor installations.