The landscape of digital commerce is undergoing a profound transformation as artificial intelligence and sophisticated automation tools provide cybercriminals with the means to conduct fraud at an unprecedented scale. While the foundational tactics of ecommerce theft—such as credit card skimming, account takeovers, and fraudulent refund requests—have existed for decades, the integration of generative AI is enabling bad actors to execute these schemes with significantly higher velocity and success rates. Industry analysts project that as merchants move toward 2027, the frequency of these attacks will likely escalate, forcing a fundamental shift in how digital retailers approach loss prevention and consumer authentication.
The Escalation of Digital Fraud: A Chronology of Risk
The trajectory of ecommerce fraud has been marked by a transition from manual, human-led exploits to high-frequency, automated campaigns. In the early 2010s, fraud was largely opportunistic, relying on stolen credentials sold in dark web marketplaces. By the late 2010s, the emergence of bot networks allowed for "credential stuffing" attacks, where automated software would test millions of username-password combinations against merchant databases.
As of late 2025, the Merchant Risk Council (MRC) reported a concerning uptick in fraudulent activity. According to the Q4 2025 Global Payments and Fraud Report, the average percentage of fraudulent ecommerce orders climbed from 3.0% to 3.5% year-over-year. While a 0.5% increase may appear marginal in isolation, the compounding financial impact is severe. For a mid-sized merchant processing 2,500 orders monthly with an average order value of $50, this shift represents an annual revenue loss increase of thousands of dollars, excluding the hidden costs of chargeback fees, administrative labor, and potential merchant account penalties.
This progression suggests a clear trend: as defensive AI tools become more adept at flagging traditional fraud patterns, criminals are using generative AI to create more "human-like" deceptive signals, effectively masking their activities as legitimate consumer behavior.
Breakdown of the Top Five Fraud Vectors
The current threat environment is dominated by five primary categories of fraud, each of which is being amplified by contemporary technological advancements.
1. The Persistence of Refund Abuse
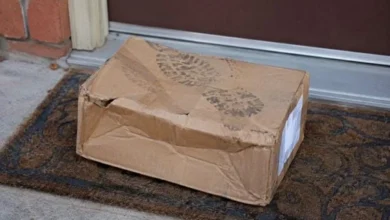
Refund and return policy abuse currently ranks as the most prevalent form of fraud, impacting approximately 41% of merchants. Historically, this involved a customer claiming a package was lost or damaged to secure a refund while keeping the goods. Today, generative AI has simplified the fabrication of evidence. Fraudsters can now use AI image-generation tools to create highly convincing photographs of "damaged" goods or use large language models (LLMs) to draft professional, high-pressure communication that mimics legitimate consumer complaints. This creates a "trust tax" for retailers, who must choose between alienating honest customers with rigid return policies or sustaining direct financial losses from sophisticated fabricators.
2. Real-Time Payment Vulnerabilities
Real-time payments—defined by near-instantaneous settlement—have revolutionized consumer convenience but have introduced a significant security gap. With 38% of merchants reporting issues, this payment method is increasingly targeted because of its irreversibility. Unlike traditional credit cards, which offer a buffer period for dispute resolution, real-time transfers are effectively "final" the moment they hit the recipient’s account. Criminals utilize "authorized push payment" (APP) scams, where AI-generated voice or video deepfakes are used to impersonate bank representatives or authority figures, coercing victims into initiating the fraudulent transfer themselves.
3. Credential Theft and Account Takeover (ATO)
Credential theft remains a cornerstone of cybercrime, affecting 37% of businesses surveyed. By impersonating trusted entities—logistics companies like FedEx or financial institutions—criminals harvest login credentials. The danger here lies in the "legitimacy" of the account; an order placed from a long-standing, verified customer account is significantly less likely to be flagged by standard fraud detection algorithms than a new, guest-checkout order. As AI automates the creation of phishing sites and personalized social engineering lures, the barrier to entry for ATO attacks has plummeted.
4. The Automation of Card Testing
Card testing, or "carding," is the practice of using automated scripts to test stolen credit card data on ecommerce sites to verify which cards are still active. With 33% of sellers experiencing this, it remains a persistent nuisance. Modern botnets can now execute thousands of micro-transactions per minute across multiple retailers. Beyond the immediate financial impact, this activity floods merchant checkout systems with high-velocity traffic, often leading to site performance degradation and triggering automated blocks from payment gateways, which can inadvertently shut down legitimate sales.
5. Identity Theft and Synthetic Identities
Perhaps the most complex challenge for future retail is the rise of synthetic identity fraud, reported by 31% of merchants. Rather than stealing an existing person’s identity, criminals use AI to synthesize a new persona by combining real data (such as a leaked Social Security number) with fabricated information. These "synthetic shoppers" are difficult to detect because they do not have a corresponding victim reporting the fraud. By building a fake credit history over time, these personas can eventually make large-scale fraudulent purchases, leaving merchants with no recourse for recovery.
Strategic Implications and Industry Response
The broader implications of these trends suggest that the "passive" fraud prevention era is coming to a close. Merchants can no longer rely on simple rules-based filters, such as blocking specific IP addresses or checking for mismatched billing and shipping addresses, as these methods are easily bypassed by sophisticated AI proxies and residential VPNs.
Industry leaders are increasingly calling for a shift toward "behavioral biometrics"—a method of analyzing how a user interacts with a device (e.g., mouse movement patterns, typing speed, and device orientation) to confirm identity. Furthermore, the push for stronger multi-factor authentication (MFA) and hardware-based security keys is gaining momentum.
However, the cost of these implementations remains a barrier for smaller enterprises. There is a growing disparity between large retailers, which have the capital to invest in proprietary AI-driven fraud detection, and small-to-medium businesses (SMBs), which often rely on third-party plugins that may struggle to keep pace with evolving threats.
Future Outlook: 2027 and Beyond
As we approach 2027, the retail sector is braced for a technological "arms race." The democratization of AI tools means that even low-level criminals now possess capabilities previously reserved for state-sponsored actors. The efficacy of fraud prevention will rely heavily on cross-industry collaboration, where merchants share anonymized threat data to build more robust, predictive models.
Moreover, regulatory bodies are beginning to take note. Governments are under pressure to establish clearer liability frameworks for real-time payments, potentially forcing financial institutions to implement more stringent verification protocols before funds are moved. For the individual merchant, the focus must shift from reactive recovery to proactive friction—implementing security measures that are sophisticated enough to deter automated threats while remaining fluid enough to ensure that the conversion rate of legitimate customers is not compromised.
In conclusion, the intersection of AI and commerce is a double-edged sword. While AI offers retailers unprecedented opportunities for personalization and operational efficiency, it simultaneously provides the architecture for a more aggressive, automated, and pervasive fraud ecosystem. Success in the coming years will depend on a merchant’s ability to balance the necessity of robust security with the fundamental need for a seamless, trustworthy customer experience.
Related posts: