Microsoft Corp. Issues Record-Breaking Security Patch Bundle Addressing Nearly 1,000 Vulnerabilities

In a historic escalation of cybersecurity maintenance, Microsoft Corp. released its largest single batch of security updates in company history this month, addressing at least 974 distinct vulnerabilities across its Windows operating systems and associated software ecosystem. This massive deployment, arriving as part of the company’s standard "Patch Tuesday" cycle, underscores a rapidly changing landscape in software security where the integration of artificial intelligence is fundamentally altering both the speed of vulnerability discovery and the operational burden on corporate information technology departments.
A Chronology of Escalating Patch Volume
The sheer scale of this month’s release represents a significant departure from previous industry norms. While Microsoft has historically managed vulnerability disclosures through a predictable monthly cadence, the volume of identified flaws has trended sharply upward. To contextualize the current situation, one must look at the recent trajectory of Microsoft’s security disclosures.
In July 2026, Microsoft set a then-unprecedented record by issuing patches for 570 vulnerabilities. September’s release of nearly 1,000 patches obliterates that figure, bringing the total number of security flaws addressed by the company so far this year to over 2,600. For perspective, the previous record for an entire calendar year was set in 2020, with 1,245 documented vulnerabilities. With three months remaining in 2026, the company is on track to more than double its highest historical annual volume, signaling a paradigm shift in the software development and auditing lifecycle.
The Impact of AI-Assisted Vulnerability Research
Industry experts point to the widespread adoption of artificial intelligence in security research as the primary catalyst for this volume explosion. Security researchers, white-hat hackers, and even malicious actors are increasingly utilizing generative AI and machine learning models to automate the discovery of software weaknesses. These tools can parse millions of lines of source code in a fraction of the time required by human analysts, identifying edge cases, buffer overflows, and logic errors that might otherwise remain buried for years.
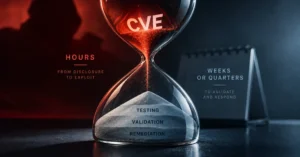
While this advancement is a boon for proactive defense, it creates a "discovery paradox." As discovery becomes automated and efficient, the output of security research—the number of CVEs (Common Vulnerabilities and Exposures)—surpasses the human capacity to test, validate, and deploy the corresponding patches. This creates a backlog that places unprecedented pressure on enterprise IT teams.
Critical Vulnerabilities and Active Exploitation
Among the 974 patches released this month, 113 have been classified as "critical." This designation is reserved for vulnerabilities that allow for remote code execution (RCE) or privilege escalation, effectively granting an attacker control over a system with minimal or no user interaction.
Of particular concern are two specific "zero-day" flaws, CVE-2026-81963 and CVE-2026-85880, which Microsoft confirmed are already being exploited in the wild. These vulnerabilities allow attackers to elevate their privileges on affected Windows systems, turning standard access into administrative-level control.
Furthermore, security researchers have highlighted CVE-2026-69730, a critical DNS weakness affecting Windows Server 2012 and later, as well as Windows 10. The vulnerability allows an unauthenticated attacker to compromise a system by sending a specially crafted packet. Because the attack requires no user interaction, it is categorized as highly likely to be weaponized. Similarly, CVE-2026-69829, a remote code execution flaw in the Windows Shell, has been assigned a CVSS (Common Vulnerability Scoring System) base score of 9.8 out of 10. Given that it requires low attack complexity and no privileges, it represents a top-tier threat to enterprise networks.

The Growing Burden on Corporate Infrastructure
The operational reality for modern enterprises is becoming increasingly untenable. Tyler Reguly, associate director of security research and development at Fortra, emphasizes that the primary obstacle is not the availability of a patch, but the rigorous testing required to ensure that updates do not break critical business applications.
"It is time to put our CISOs and CSOs on notice," Reguly stated. "The complexity of the modern enterprise stack means that a single OS patch can inadvertently disable third-party software, financial systems, or legacy databases. We are seeing a trend where teams are forced to work weekends and overnight hours just to maintain basic security hygiene. Organizations need to rethink their resource allocation, their budgets, and the way they support the personnel tasked with these high-stakes deployments."
This sentiment is echoed across the industry. Major software vendors including Cisco, Oracle, Google, and Adobe are facing similar surges in patch volume. Google, for instance, has recently announced plans to accelerate its security update cadence to a bi-weekly cycle, further compressing the window for enterprise testing.
Strategic Prioritization: Needles in the Haystack
Despite the alarming volume of patches, Satnam Narang, senior staff research engineer at Tenable, cautions against panic-driven deployments. He suggests that while AI is effectively finding more vulnerabilities, the percentage of these flaws that pose a legitimate, immediate risk to the average organization remains relatively low.
"AI-assisted vulnerability discovery in 2026 is creating larger haystacks, but it isn’t necessarily finding more needles," Narang explained. "For an organization, the goal shouldn’t be to install every single patch the moment it drops. Instead, the focus must be on risk context. IT teams need to determine which vulnerabilities are actually reachable, which ones are being actively exploited, and which ones exist on critical infrastructure. Prioritizing remediation based on threat intelligence is no longer a luxury; it is the only way to manage this volume."
Implications for the Future of Enterprise Security
The current state of software security suggests several long-term implications for the industry:
- Automation of Patch Management: As the number of patches continues to grow, manual deployment will become obsolete. Enterprises will likely rely more heavily on automated patch management and orchestration platforms that use AI to predict potential system conflicts before they occur.
- Shift-Left Security: Vendors will face mounting pressure to implement "secure by design" principles. If the volume of vulnerabilities continues to climb, the industry may see a regulatory push toward stricter coding standards to mitigate flaws before software is even released to the public.
- The Talent Gap: The exhaustion of security teams is a growing concern. If the current trend of weekend-heavy maintenance continues, companies may face high turnover rates among IT staff, further exacerbating the security risks caused by the talent shortage.
- Third-Party Compatibility: The ongoing struggle with patch-related system failures may lead to a greater push for modular operating systems or sandboxed environments where security updates can be applied to core components without affecting the broader application layer.
Guidance for Administrators and Users
For standard users, the mandate remains simple: enable automatic updates. While the patch volume is high, the risk of ignoring these updates—particularly given the two actively exploited zero-days—far outweighs the inconvenience of a system restart.
For enterprise administrators, the strategy must be more nuanced. Experts recommend monitoring resources such as the SANS Internet Storm Center, which provides detailed, severity-ordered breakdowns of every patch release. Furthermore, community-driven resources like AskWoody offer crowd-sourced insights into which patches are causing "breakage" in real-world environments, allowing administrators to avoid updates that might lead to immediate, large-scale downtime.
Ultimately, September 2026 will be remembered as a tipping point in the relationship between software vendors and the users they protect. As the digital infrastructure becomes more complex and the mechanisms for uncovering its flaws become more efficient, the responsibility for securing the modern world has transitioned from a manageable maintenance task into a relentless, high-stakes operational campaign. Organizations that fail to adapt their processes to this new reality—by investing in automated testing, prioritizing risk-based patching, and supporting their overextended IT staff—risk finding themselves increasingly vulnerable in an era of near-constant cyber-threats.
Related posts: